Sixteen Billion Reasons to Protect Your Online Identity
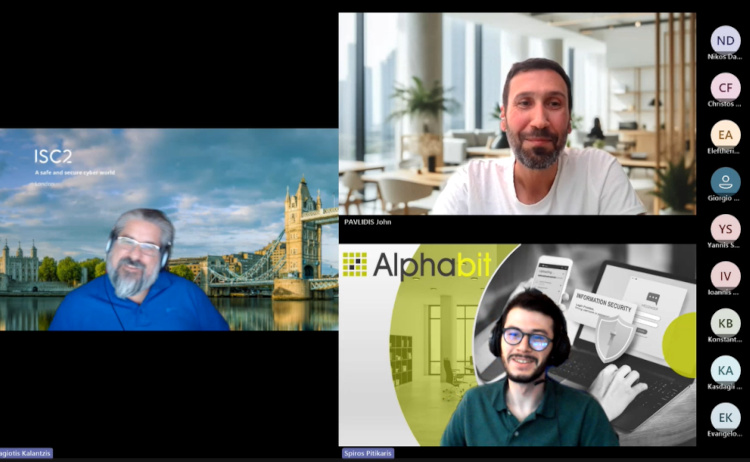
During our today’s panel on identity security and digital access management, we had the opportunity to explore one of the most crucial and evolving areas of cybersecurity. What emerged clearly from the discussion is that identity security is no longer a purely technical concern; it has become a strategic enabler of trust, resilience, and long-term business continuity. In other words, Identity Security is a Strategic Business Enabler
Where does an organization begin?
One of the key questions raised was: What are the first steps for a company looking to strengthen its identity security? The consensus among the panelists was that everything starts with visibility; understanding who has access to what, and why. Mapping all digital identities (human and machine), implementing multi-factor authentication (MFA), and applying the principle of least privilege were identified as foundational steps.
However, panelists also warned against the trap of “technology-first thinking.” Identity security cannot be solved simply by deploying another tool. Without clear policies, regular access reviews, and ongoing governance, technology alone will not deliver sustainable protection.
The major misconception: “It’s an IT issue”
Another strong theme was the persistent misconception that identity security is solely the responsibility of the IT department. In reality, identity now defines the new perimeter of cybersecurity, and it touches every function:
- Management, responsible for governance and accountability;
- Human Resources, managing the lifecycle of employees and contractors;
- Legal and Compliance teams, ensuring adherence to regulations.
Identity management is, above all, a matter of corporate governance and shared responsibility.
Beyond defense: the strategic value of identity
The discussion also highlighted the positive business outcomes that stem from a mature identity strategy. These include lower operational costs, simplified compliance with frameworks such as ISO 27001, GDPR, and NIS2, streamlined onboarding/offboarding processes, and enhanced user experience through single sign-on (SSO).
But perhaps most importantly, strong identity security builds trust; with customers, partners, and employees alike. Trust, in turn, becomes a competitive advantage.
The human factor
Finally, the panel emphasized the critical role of education and security culture. Despite rapid technological progress, the human element remains the decisive factor in cybersecurity.
Training should not be treated as a formality but as an investment in organizational resilience.
When people understand the why behind security measures, they become allies – not obstacles – in the protection effort.
A strong security culture transforms awareness into shared responsibility.
Closing thoughts
Our discussion made one thing clear: identity security is not a one-time project, but an ongoing strategic journey.
The challenge for modern organizations is not only to safeguard their data, but to build and sustain digital trust at every point of interaction.
And that journey, inevitably, begins with identity.