The Malware that Redefined Power, Precision, and Cyber-Physical Warfare
A Quiet Discovery that Changed the Meaning of Cybersecurity
In 2010, security researchers began analyzing a strange piece of malware that behaved unlike anything they had seen before. It spread through Windows systems, used multiple zero-day vulnerabilities, and carried valid digital certificates stolen from legitimate companies. Yet its behavior seemed oddly restrained. It did not steal banking credentials; it did not launch ransomware attacks; it did not flood networks with noise. Instead, what it later named Stuxnet cyber weapon, waited.
At first, many analysts assumed they were dealing with another sophisticated espionage platform. Advanced persistent threats had already become part of the strategic vocabulary of cybersecurity. Nation-states had begun treating cyberspace as an operational domain for intelligence gathering and influence operations. But Stuxnet pushed far beyond espionage.
It targeted machinery. And in doing so, it changed cybersecurity forever.
The Real Target was Hidden Deep Inside Iran
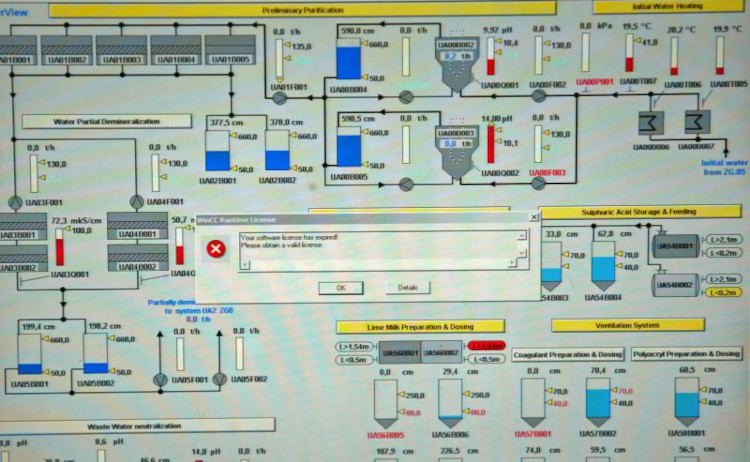
The malware’s true destination was the Natanz nuclear facility, a heavily protected uranium enrichment facility in Iran. Inside the plant, thousands of centrifuges spun at extremely high speeds to enrich uranium. Those centrifuges relied on industrial control systems built with software and programmable logic controllers from Siemens.
Stuxnet did not attack those systems directly. It moved carefully through intermediate environments first. It spread through USB devices, crossed air-gapped networks, and searched infected machines for highly specific industrial configurations. Only after finding the exact target conditions did the malware activate its payload.
That level of precision stunned the cybersecurity community.
Most malware operates opportunistically. Stuxnet cyber weapon behaved more like a covert military operation. Its developers clearly understood centrifuge physics, industrial engineering, and operational workflows inside enrichment facilities. They also understood how human operators monitored industrial processes.
The malware manipulated centrifuge speeds to create mechanical stress and gradual degradation. At the same time, it fed normal telemetry back to monitoring consoles. Engineers saw stable operations while the physical systems underneath them slowly destabilized.
Stuxnet cyber weapon attacked trust as much as machinery.
Code Became a Physical Weapon
Before Stuxnet cyber weapon, many discussions about “cyber warfare” remained theoretical. Security professionals understood that industrial systems contained vulnerabilities, but few had seen malware produce deliberate physical destruction with such precision and control.
Stuxnet changed that overnight. The operation proved that software could move beyond data theft and digital disruption. Code could now alter physical reality. Malware could destroy equipment, sabotage industrial processes, and achieve strategic geopolitical objectives without a missile strike or military invasion.
That realization carried enormous implications. Governments immediately recognized the strategic value of cyber-physical operations. Critical infrastructure operators began reassessing long-standing assumptions about isolation and safety. Industrial security moved from a niche discipline into a central national security concern.
Cybersecurity no longer belonged only to IT departments. It became a matter of statecraft.
The Sophistication Was Extraordinary
Even today, Stuxnet remains one of the most sophisticated malware platforms ever discovered in the wild.
The operation used multiple zero-day exploits at the same time, something extremely rare even among elite threat actors. It employed stolen digital certificates to avoid detection. It contained highly specialized PLC rootkit functionality that manipulated industrial logic while hiding the changes from operators and engineers.
Most remarkably, the malware included strict activation criteria. It ignored systems that did not match the intended target profile. That restraint reduced the chances of discovery and minimized unintended disruption.
This was not reckless malware. It was engineered with discipline.
The operation also reflected close coordination between cyber operators and subject matter experts. The developers needed detailed intelligence about centrifuge configurations, industrial protocols, operational timing, and facility architecture. That level of integration strongly suggested nation-state sponsorship.
Public reporting has widely linked the operation to the National Security Agency and Israel, reportedly under a covert initiative known as Olympic Games. Although no government has formally acknowledged responsibility, most strategic analysts consider the attribution credible.
Regardless of attribution, the broader message became unmistakable. Major powers had operationalized offensive cyber weapons capable of causing physical damage.
The Myth of the Air Gap
One of Stuxnet’s most important lessons involved the failure of the so-called “air gap.”
For years, industrial operators believed physical network separation provided strong protection against cyber threats. If critical systems remained disconnected from the internet, many assumed attackers could not reach them.
Stuxnet exposed the weakness in that assumption. The malware moved through removable media and human operational behavior. It exploited trust relationships between systems. It leveraged normal maintenance and engineering workflows to cross isolated environments.
The attack demonstrated a critical truth that still shapes modern industrial security strategy: Air gaps reduce exposure, but they do not eliminate risk. Human activity always creates pathways into supposedly isolated environments. Determined adversaries understand that reality well.
The Birth of Modern Cyber-Physical Conflict
Stuxnet did more than sabotage centrifuges. It introduced a new model of conflict.
Traditional cyber operations focused on espionage, surveillance, or disruption. Stuxnet pursued strategic physical effects while remaining covert for long periods of time. It operated below the threshold of conventional warfare and created ambiguity around attribution and escalation.
That model now appears across the modern threat landscape.
Campaigns targeting power grids, oil and gas infrastructure, transportation systems, and manufacturing facilities all reflect the strategic logic that Stuxnet helped normalize. Malware families such as Industroyer and Triton demonstrated that adversaries continue to invest heavily in operational technology attacks.
Critical infrastructure has become a contested battlespace.
And the attack surface continues to expand.
Industrial environments now integrate cloud connectivity, remote operations, IoT devices, and increasingly autonomous systems. Organizations gain efficiency and visibility through digital transformation, but they also inherit new forms of operational risk.
The convergence of IT and OT has erased many of the boundaries that once separated corporate networks from physical processes.
Why Stuxnet Still Matters
More than fifteen years later, Stuxnet still serves as a defining case study for senior cybersecurity professionals because it forced the industry to confront uncomfortable realities that remain unresolved today.
It showed that:
- Sophisticated adversaries will invest years into highly specific targets
- Operational technology environments require dedicated security strategies
- Physical consequences can emerge from digital compromise
- Deception inside industrial systems may remain invisible for extended periods
- Cyber operations can achieve geopolitical objectives without conventional military force
Most importantly, Stuxnet revealed that modern civilization depends on systems that attackers can manipulate remotely and quietly.
Power generation. Water treatment. Healthcare infrastructure. Transportation networks. Manufacturing systems. Energy pipelines.
All of them rely on industrial processes controlled by software.
And every one of those systems now sits within the broader threat landscape of cyber conflict.
The Legacy of Stuxnet
Stuxnet occupies a unique place in cybersecurity history because it marked the moment when cyber warfare stopped being theoretical.
The malware demonstrated that code could produce kinetic effects with precision, patience, and strategic intent. It forced governments and security leaders to rethink the relationship between cybersecurity and national security. It also accelerated investment in industrial defense, threat intelligence, operational resilience, and cyber-physical security research.
But perhaps the most important lesson is simpler and more enduring.
Stuxnet proved that the most dangerous cyber weapons may not announce themselves loudly or spread indiscriminately across the internet. The most dangerous operations often behave exactly as designed. They remain focused, disciplined, and nearly invisible until the damage has already begun.
That reality continues to shape cybersecurity strategy today.
And it likely will for decades to come.