The Compliance Illusion
When Security Becomes Urgent, for the Wrong Reasons
Most companies don’t wake up one morning and decide they need a Chief information Security Officer (CISO) because the threat landscape has shifted or because their architecture is quietly accumulating risk. They hire a CISO the way they hire a tax advisor right before an acquisition: not because the business suddenly discovered a love of discipline, but because the business discovered friction. The company grows, the sales team starts reaching further upmarket, and the conversations get more serious. Procurement joins the calls. Legal appears. Security questionnaires land in inboxes with the weight of an unspoken ultimatum. And somewhere in the middle of a promising deal, a buyer asks, almost casually, whether you have SOC 2, ISO 27001, a penetration test report, a set of formalized policies. Some proof they can trust your organization with their data. That’s usually when “security” becomes urgent and the compliance vs security debate begins.
Not because a breach just happened, or because engineers are begging for time to refactor brittle systems. Not even because leadership has read enough postmortems to understand how quickly a single misconfiguration can become a headline. It becomes urgent because revenue is now blocked by a certificate. The threat that finally moves security up the priority list is not an attacker. It’s a stalled pipeline. A quarter in jeopardy. A deal that won’t close until someone can attach a PDF.
The Rise of Compliance Theater
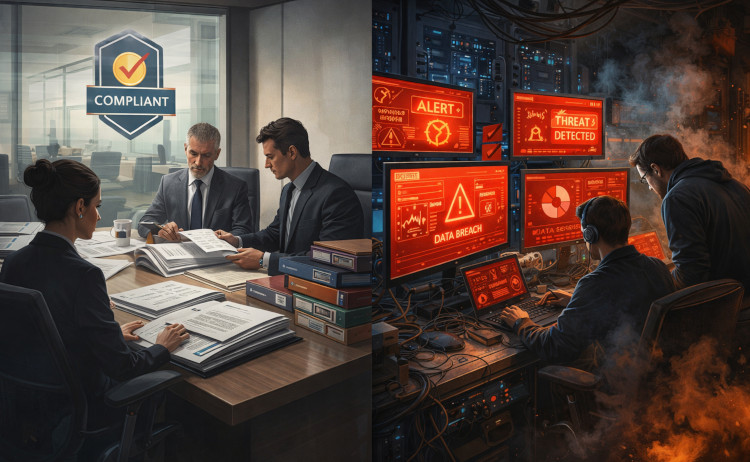
So the company hires a Chief information Security Officer (CISO), and almost immediately the theater (compliance vs security) begins.
A security program, at least in its most visible form, materializes with impressive speed. Policies appear, neatly named and versioned, as if they’ve been waiting in a drawer all along. Processes are documented. Controls are mapped to frameworks. There are meetings with auditors, then more meetings to prepare for the meetings. Someone builds a repository of evidence. Someone else builds a slide deck. The organization learns a new vocabulary—risk registers, control owners, exceptions, compensating controls. Terms that sound like certainty even when the underlying reality is still messy. A badge shows up on the website. A report gets shared with customers under NDA. Leadership exhales, because the company now has a thing it can point to, a signal it can send, a stamp that says “we take security seriously.”
And maybe, on paper, it does. But security was never meant to live on paper.
The Dangerous Substitution
The problem is not that compliance is useless. Compliance can be a forcing function, a way to introduce discipline where there was none, and in mature organizations it can serve as a valuable baseline. The problem is the quiet substitution that happens when the document becomes the product, when the audit becomes the milestone, when what we can prove instead of what we can prevent becomes the program success metric. Companies start to mistake the ability to demonstrate controls for the ability to withstand an adversary. They confuse “we have a policy” with “we have a practice,” and they confuse “we passed” with “we’re safe.” They confuse compliance vs security.
Attackers do not read your policy folder. They don’t care that you have scheduled your access review for Q4 or that you store your incident response plan in a shared drive. Attackers exploit the seams. Where speed outruns rigor, or design decisions were made under deadline pressure. Where a shortcut becomes permanent because it works well enough, or a service account has more privilege than it needs because nobody wanted to break production. They exploit assumptions, not documentation. And when those assumptions fail, they fail in real systems, with real customers, in real time, far away from the clean edges of an audit report.
Where Security Actually Lives
That’s why the organizations with the strongest security posture rarely talk about security as a department, or a quarterly exercise, or an annual ritual performed in the weeks before auditors arrive.
They talk about it as a way of building. Security shows up in the moment an engineer chooses an approach for authentication. It shows up in the debate about what data should be collected and retained. In the decision to ship a feature now or redesign it so it fails safely later. It shows up when a developer reaches for a dependency and pauses long enough to ask whether it’s maintained, whether it’s trusted, whether it’s necessary. It shows up when on-call teams treat anomalies as signals instead of noise, and when postmortems aren’t an exercise in blame but in learning. In other words, it shows up as culture: not a slogan on a slide, but a set of instincts that shape thousands of small choices the company makes every day.
And culture is not something you can bolt on after the fact.
The Leadership Signal
This is where senior leadership matters more than most organizations admit. Because whether security becomes a living, breathing part of the company – or a ceremonial function performed to satisfy customers – depends on what leaders reward. If leadership introduces security primarily as a revenue enabler, the message to teams is unmistakable. Do what it takes to get the certificate, keep the deal moving, and don’t let this slow you down. Teams respond rationally. Security becomes the responsibility of “the security team.” It becomes something you remember before audits. It becomes a set of constraints to negotiate around. Even the most capable Chief information Security Officer (CISO) cannot reverse that gravity alone, because the CISO doesn’t set the company’s incentives; leadership does.
The Chief information Security Officer (CISO) as a Change Agent
In that environment, the role of the Chief information Security Officer (CISO) quietly collapses into something smaller than it should be: a compliance executive with a security title, an expert at translating messy reality into acceptable evidence. And to be clear, that work is hard, and sometimes necessary. But it is not the same as making the business safer. It is not the same as reducing the blast radius of inevitable mistakes. It is not the same as building systems that degrade gracefully under attack rather than catastrophically under pressure.
The best CISOs I’ve seen – especially in product-led companies where engineering is the engine of growth – don’t win by being the “Department of No.” They win by making security feel like craft, like professionalism, like a mark of quality rather than a tax, giving teams tools, patterns, and paved roads that make the secure path the easy path. Furthermore, they turn vague mandates into practical guidance, building relationships with product and engineering leaders so security is present at the design table, not summoned at the end as an approver of last resort. They help the organization make trade-offs honestly; naming risk, quantifying impact, choosing deliberately, rather than hiding behind checklists.
Making Security Something Teams are Proud Of
And when that happens, something interesting changes inside a company.
Security stops being scary, because it isn’t treated as a specter that appears only when something goes wrong. It stops being bureaucratic, because it isn’t defined primarily by paperwork. At the same time, it becomes something teams can be proud of. A characteristic of the product, woven into the design the same way performance, reliability, and usability are. It becomes a source of credibility, not just in the market, but internally, one more signal that the organization is building something it expects to last.
A Question for the Executive Team
Maybe that’s the pivot leaders should be making now. Not “how quickly can we get certified”, but “what kind of company are we becoming as we scale?” Not “what will satisfy procurement,” but “what will withstand reality?” Because the truth is that if security lives only inside compliance reports, it’s already late. The report will always trail the system. The badge will always lag behind the architecture. And the audit will always arrive after the stakeholders already have made the decisions that mattered.
So yes, get the certifications. Close the deals. Meet the expectations of enterprise buyers. But don’t confuse the proof of security with security itself. A PDF can open doors, but it cannot protect what’s behind them.
Only culture can. Compliance vs security is not an actual trade-off